Document audio, transcript, metadata, model, storage and system-action paths.
Security & governance
Trust is an operating model—not a feature badge.
Define where data moves, who can act, what is retained, how changes are tested and when a person takes over. Then produce the evidence reviewers need.
Controls designed into every conversation
Identity, policy, encryption, audit and human approval are operating layers—not launch-day additions.
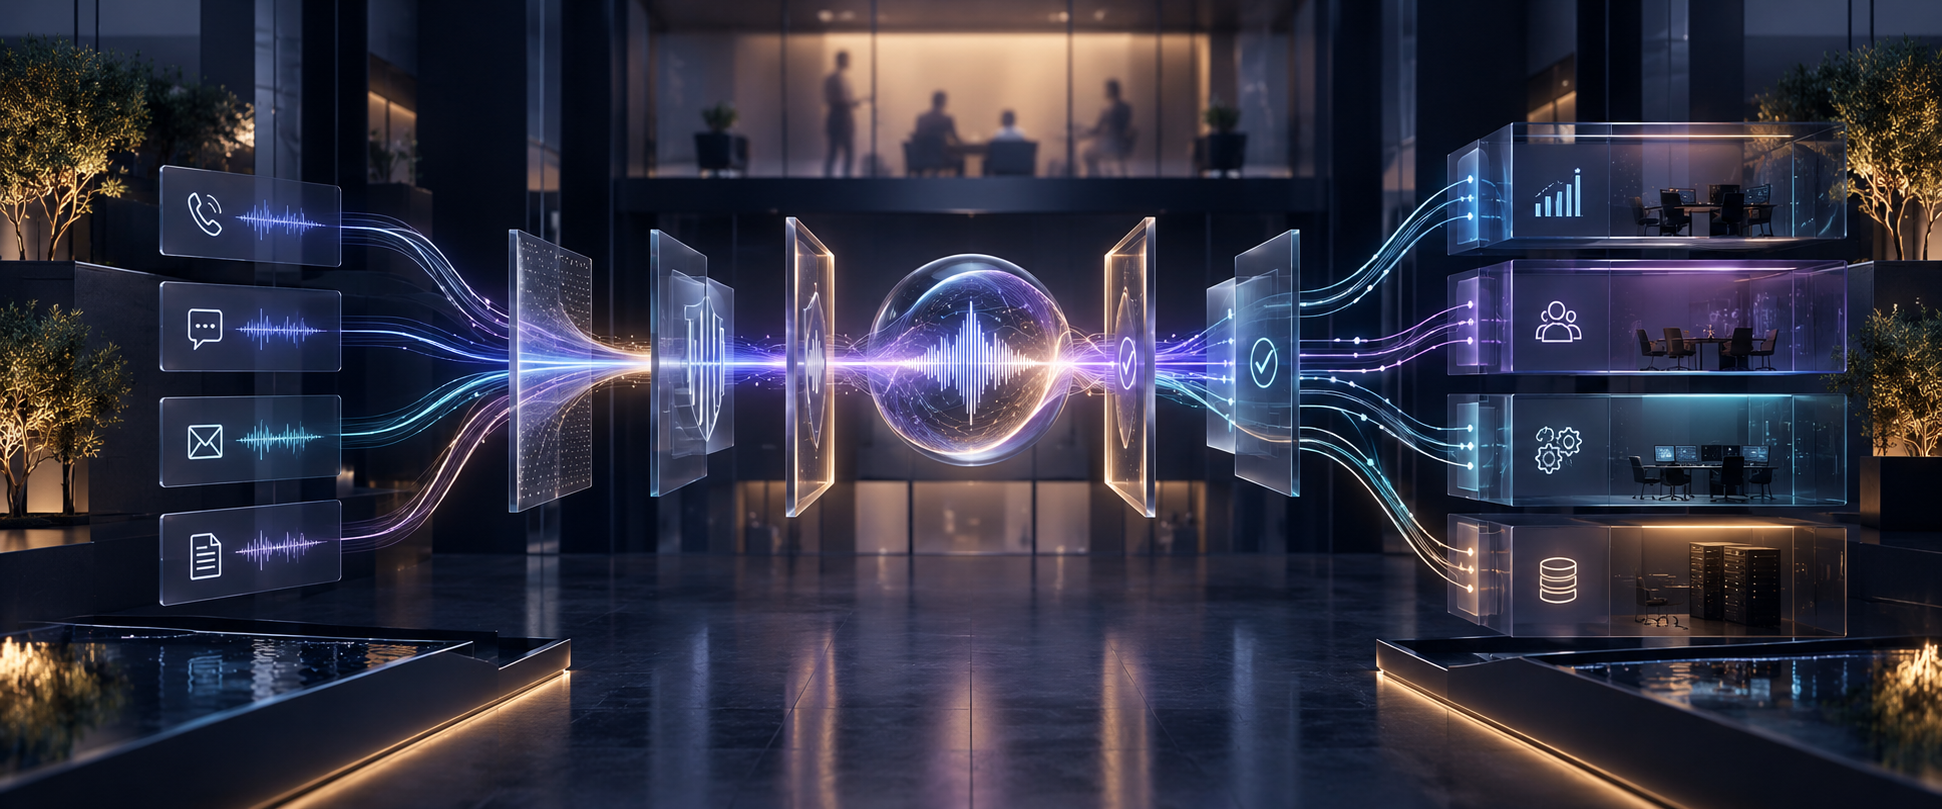
Governed by design
Every conversation crosses explicit control points before it reaches a business system.
Control framework
Questions answered
before production.
The exact controls depend on the use case and environment. We do not claim certifications the deployed service has not earned.
Separate caller verification, agent identity and system permissions. Scope every tool.
Select regions, vendors or self-hosted components against the required data boundary.
Protect data in transit and at rest; manage credentials outside prompts and source code.
Set distinct policies for recordings, transcripts, traces, evaluations and business records.
Collect only what is needed; redact or tokenise sensitive values where the workflow allows.
Define transfer, approval, shutdown and post-call review for risk and uncertainty.
Retain the inputs, instructions, tool calls, outputs and versions needed to explain an outcome.
Test normal, adversarial, ambiguous and failure scenarios before expanding traffic.
Version prompts, policies, tools and models; test changes before promotion and preserve rollback.
Review sub-processors, terms, retention, model training, support and incident obligations.
Design timeouts, provider failure, route-around, human takeover and service-degradation modes.
Assurance pack
Evidence ready for
your review process.
We shape documentation around the questions security, privacy, legal, risk, procurement and operations actually ask.
Architecture & data flow
Components, trust boundaries, networks, vendors and information movement.
Risk & control matrix
Failure modes, mitigations, owners, tests and residual risk.
Evaluation report
Scenarios, datasets, results, limitations and launch thresholds.
Privacy inputs
Purpose, data categories, retention, access and deletion arrangements.
Runbook & incident path
Monitoring, alerting, escalation, rollback, provider failure and customer communication.
Ownership schedule
Accounts, code, configuration, prompts, evaluation assets and handover obligations.